This guide explains what Kony DBX is, how it fits into deployment workflows, and what to evaluate when choosing units or integrating suppliers. Objectively, it covers typical hardware/software considerations, procurement criteria, and operational requirements. It also includes a comparison table, a practical step-by-step checklist, and expert FAQs—helping you make defensible decisions for reliability, compliance, and maintainability.
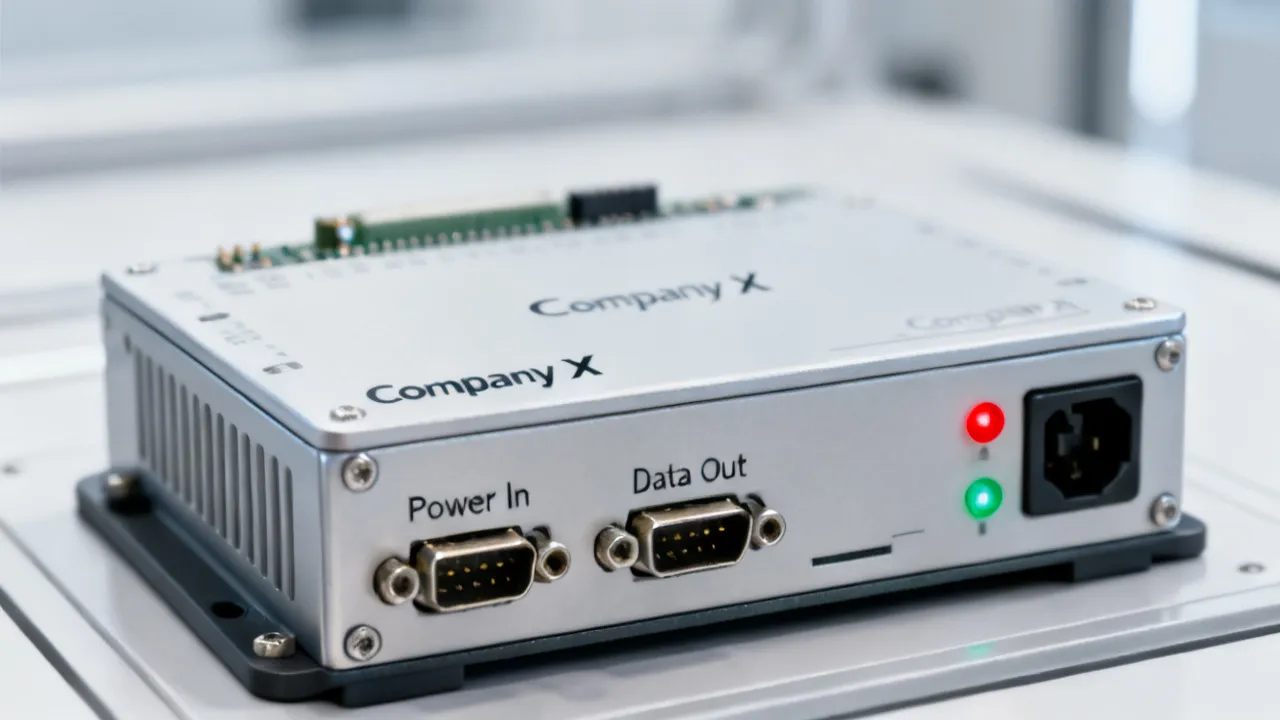
If you’re evaluating Kony DBX for system integration or operational modernization, focus first on compatibility, reliability under real workload conditions, and the evidence you can obtain from the supplier. In practice, many projects succeed or fail less due to “feature lists” and more due to how thoroughly integration assumptions are validated—interfaces, mounting/enclosure needs, lifecycle support, and test documentation.
In an expert procurement and integration lens, the very important question is not only what a Kony DBX unit can do, but whether your organization can demonstrate that it will behave predictably when connected to your existing environment—network topology, power constraints, environmental exposure, security controls, and maintenance workflows.
Modern deployments also raise expectations beyond connectivity. Stakeholders typically want operational observability, consistent and secure update pathways, auditable change history, and clear failure-mode behavior. If you cannot answer how Kony DBX signals health issues, how it logs diagnostic events, and how it recovers from partial failures, you may technically “integrate” it but still fail operational readiness and long-term maintainability goals.
Therefore, the most important success factor is not “buying a device.” It is building a repeatable integration package around the device: controlled configuration, verified interfaces, known error handling behavior, monitored health signals, secure lifecycle processes, and a documented rollout plan that includes acceptance testing and post-deployment validation.
The term Kony DBX is commonly used as a reference label in engineering and procurement contexts. While exact specifications depend on the precise model or configuration, “DBX” typically suggests a device or platform line used to support broader system functions such as connectivity, control, diagnostics, or operational data exchange. In objective terms, buyers should treat any product name as an entry point and then request the underlying artifacts: technical datasheets, interface matrices, firmware/software release notes, environmental ratings, compliance evidence, and warranty/support terms.
Because the market can include multiple revisions or OEM/ODM rebrands, relying on informal descriptions is risky. A defensible approach is to align your requirements (interface types, throughput expectations, security policies, maintenance SLAs) with the Kony DBX documentation package and perform integration verification using a test plan.
To make that approach practical, procurement and engineering teams should jointly define a “configuration baseline” before ordering. A configuration baseline typically includes: the exact part number and revision; firmware and software versions; hardware accessory selection; any required licenses; default network settings or provisioning method; and the intended configuration profile used in your application. If the supplier cannot provide evidence or documentation for that baseline, you may encounter a scenario where the shipped unit differs from what was tested.
Even when the supplier provides documentation, you should verify how the documentation ties to the shipped revision. For instance, interface capabilities may differ across hardware revisions, while security features may be enabled/disabled by software version. Similarly, environmental ratings might assume a specific enclosure, cooling method, cable routing, or installation orientation. Your integration plan should capture these assumptions explicitly and then validate them.
To reduce uncertainty, prioritize the following in order:
Because integration is where risk concentrates, you should treat each area as a measurable requirement with evidence. A useful pattern is to convert each evaluation area into a set of questions and acceptance criteria. For example, for interface compatibility, acceptance criteria might include “the unit supports protocol X over transport Y at throughput Z with specified timeout behavior” and evidence might be “interface test report” or “validated lab results tied to firmware version.” For security, criteria might include “credentials cannot be extracted without authorization” and evidence might include “secure boot documentation,” “update signing approach,” and “role-based access details,” along with how audit logs are emitted.
Additionally, you should consider integration boundaries. Many devices can technically communicate, but integration failures happen at boundaries: network address translation, routing changes, firewall rules, VLAN tagging, MTU mismatches, DNS dependencies, certificate trust chains, or time synchronization drift. Therefore, the supplier should help you understand what network services are assumed and what the device tolerates when those services are unstable.
When you source Kony DBX, the supplier selection process should mirror how you would evaluate a system-critical component supplier. A good supplier can answer integration questions without evasiveness, provide traceable part numbers, and supply evidence of compliance and testing.
From an industry expert perspective, due diligence should include:
To strengthen due diligence, you should also evaluate the supplier’s responsiveness and technical depth during pre-sales. If the supplier’s early answers are generic, your project may pay later in the form of repeated clarifications and rework. Conversely, suppliers with strong documentation practices often demonstrate readiness by providing structured interface matrices, release notes, and clearly labeled configuration parameters.
Another due diligence element is whether the supplier can support a configuration lock and bill-of-material governance model. In practice, many procurement failures occur because product ordering processes drift over time. For example, a part number remains the same but a revision changes due to manufacturing updates, causing behavior changes. Request written confirmation that changes will be communicated through PCNs and that the supplier can provide a mapping of revisions to features.
You should also evaluate whether the supplier can provide a testing or pre-qualification unit for integration verification. In many deployments, the single best risk-reduction tool is a controlled bench test using the exact part number and software baseline you plan to order. If the supplier can provide that unit (or provide a mechanism for you to validate with a certified unit), you can often detect interface or diagnostics mismatches early.
Many buyers ask for a “price” for Kony DBX before they have technical alignment. However, pricing is usually inseparable from configuration, quantity, shipping method, documentation package, and support terms. The very reliable strategy is to request a structured quotation that itemizes:
If a supplier cannot provide part-number-level pricing structure, you risk paying for non-comparable packages. For procurement governance, insist on an apples-to-apples comparison across vendor quotes.
Additionally, you should model total cost of ownership (TCO) rather than only unit cost. In device deployments, the cost of ownership often spikes due to: support downtime during RMAs, time spent troubleshooting due to insufficient diagnostics, the cost of rework if configuration assumptions were incorrect, the cost of security remediation if update mechanisms are inadequate, and the cost of extended lead times if spares cannot be sourced. TCO also includes the cost of labor for training and acceptance testing.
A mature pricing approach includes a cost comparison for the “integration deliverables” as well as the hardware. For example, you might compare whether the supplier offers: detailed interface and wiring diagrams, test evidence relevant to your conditions, a structured update mechanism, and a documented diagnostic interface (logs, counters, alerts). Those items may not be explicitly priced as a separate line item, but they influence integration risk and therefore project cost.
Integration typically includes both technical and operational tasks. The technical side is about interfaces and behavior; the operational side is about monitoring, incident response, and lifecycle management.
Key technical topics to validate early:
Key operational topics to validate early:
To make integration validation more concrete, consider building a test matrix that maps your environment to device behaviors. For example:
This “environment-to-behavior mapping” helps ensure that integration is not treated as a one-time connectivity check. Instead, integration becomes an operational readiness exercise that covers the situations you actually face in production.
The following table is designed to help you compare procurement and integration options for Kony DBX in a structured way. It avoids promotional claims and instead focuses on practical, verifiable requirements.
| Category | What to Ask | Requirement/Condition | Why It Matters for Kony DBX |
|---|---|---|---|
| Part number & revision | Provide exact part number and software/firmware version baseline. | Order must match documented revision and release notes. | Prevents “works in demo, fails in production” scenarios due to configuration drift. |
| Interface matrix | Request a full interface list and supported protocols. | Interfaces must match your system’s electrical/network requirements. | Integration risk is reduced by verifying compatibility up front. |
| Environmental ratings | Provide temperature, humidity, ingress, and vibration specs (as applicable). | Chosen configuration must meet your site conditions. | Reliability improves when operating margins are known. |
| Security posture | Ask about authentication, update mechanisms, and credential storage. | Security controls must align with your internal policies. | Supports auditability and reduces vulnerability exposure. |
| Warranty & RMA | Confirm warranty length and RMA turnaround expectations. | Define acceptable downtime and response times. | Protects operational continuity if defects occur. |
| Support & lifecycle | Request lifecycle policy and end-of-support timelines. | Spare planning must be feasible for your deployment horizon. | Reduces good replacement and compliance risk. |
| Documentation pack | Provide datasheets, installation guide, and maintenance/diagnostic documentation. | Documentation must be versioned and complete. | Enables repeatable installation and easier troubleshooting. |
| Testing evidence | Request test reports or validated outcomes for relevant conditions. | Evidence must be tied to the ordered configuration. | Converts “trust” into measurable assurance. |
When you use this table as part of a procurement workstream, you should also capture the follow-up status for each row: “supplier provided evidence,” “supplier needs clarification,” or “pending internal test.” This turns evaluation into a trackable process and reduces the chance that key unknowns are discovered only after installation.
Use this step-by-step guide to structure evaluation and reduce risk when adopting Kony DBX in real operations.
To expand the value of this step-by-step guide, you can implement each step with deliverables. For example:
This “deliverable approach” is a practical method used in high-reliability procurement programs. It prevents ambiguity and helps you prove that evaluation and integration were performed with discipline.
Procurement teams increasingly treat embedded/industrial components as lifecycle assets rather than one-time purchases. This shift is reflected in how organizations manage:
These practices align with established cybersecurity and infrastructure assurance guidance published by recognized bodies such as the U.S. National Institute of Standards and Technology (NIST), including frameworks and top practices for risk management and operational security. (For general reference, see NIST publications and guidance at nist.gov.) Likewise, device procurement guidance often reflects broader principles from standards bodies such as ISO/IEC on risk and quality management.
In practical deployment programs, “standardize reliability” means adopting repeatable templates for procurement requirements and integration acceptance. For example:
This is where Kony DBX evaluation becomes easier. You are not inventing requirements each time; you are applying standardized governance to determine whether a given device fits your operational model.
Another aspect of standardization is building an “operational model” in advance. Many teams decide after deployment how they will monitor devices, who will respond to alerts, what escalation paths exist, and how updates will be performed. However, this often causes friction and delays. If Kony DBX diagnostics or health indicators are not exposed in an operationally usable way, the monitoring model may need redesign. Starting with the operational model helps prevent this mismatch.
Kony DBX is typically referenced as a device/platform name within procurement and integration contexts. Buyers evaluate it through documentation because part number revisions, firmware/software baselines, interface matrices, and environmental/security specifications determine real-world performance. A “feature list” alone rarely guarantees compatibility.
In documentation-centric evaluation, the buyer looks for specificity and version traceability: “What firmware version is tested?” “What exact hardware revision is supported?” “What connectors and pinouts are used?” “What error codes and log fields exist?” “How are updates authenticated?” “What are the documented recovery and reboot timelines?” The quality of these answers is usually what differentiates a safe procurement from an uncertain one.
Ask suppliers to quote the exact part numbers/revisions and itemize costs for accessories, documentation packages, warranty/service options, and any configuration or licensing components. Compare apples-to-apples using a structured quotation format so technical scope matches across vendors.
If you compare only unit cost, you may unintentionally select a vendor that provides fewer integration deliverables or less favorable support terms. For instance, one vendor might provide a full diagnostic log format and a guided installation package; another might provide minimal documentation. Those differences have cost implications later in troubleshooting time, RMA handling, and training overhead.
Common risks include interface mismatch (protocols or wiring assumptions), insufficient diagnostic visibility during faults, unclear update/rollback procedures, and environmental conditions that exceed the device’s operating margins. Another frequent issue is revision drift—when the shipped unit differs from what was tested.
To reduce these risks, you should insist on evidence tied to the ordered configuration. When suppliers provide test results, require them to specify the part number, revision, firmware/software version, and configuration profile used during testing. If these details are missing, treat the evidence as incomplete.
Request test reports or validation evidence tied to the specific configuration you will order. Look for documentation that addresses error handling, stress behavior, environmental readiness, and diagnostic behavior under fault conditions.
Reliability evidence can include lab-based stress tests, but it can also include operational telemetry artifacts (if available), reliability models, or documented historical incident patterns. The key is traceability: the evidence should map to your exact device baseline. If you cannot establish traceability, incorporate a risk acceptance and compensating controls—such as requiring a phased deployment, increased monitoring, or additional acceptance tests.
Training needs depend on your organization’s existing capability. At minimum, installers and operators should understand installation requirements, monitoring/diagnostic workflows, and update procedures. The supplier’s documentation pack and any onboarding support can materially reduce implementation errors.
In mature deployments, training is role-based. Installers need wiring and mechanical installation guidance. Operators need health/status monitoring and normal operating procedures. Incident responders need troubleshooting steps, log interpretation guidance, and safe recovery actions. If the supplier’s documentation does not support all roles, you may need internal training development.
Support and lifecycle commitments influence the good ability to maintain uptime. If a supplier cannot guarantee availability of spares, provide revision change management, or support timely RMA handling, the operational cost can exceed the initial unit price.
Lifecycle also affects compliance. If security vulnerabilities are discovered and the supplier cannot provide updates or patches within a reasonable timeframe, your organization might face security remediation costs or forced replacement. Therefore, lifecycle terms should be treated as an operational security requirement, not just a procurement convenience.
Ask about authentication mechanisms, credential handling, access control boundaries, logging/audit outputs, and the security properties of update processes (including how updates are validated and how rollback is performed, if supported). Ensure alignment with your internal security policies.
In security-by-design evaluation, you also ask about what happens when access controls fail or are misconfigured. For example, does the device expose services in insecure default modes? Can you disable unused services? What is the credential reset procedure? Are there documented recovery steps that do not require unsafe workarounds? Those questions often determine whether the device is safe to operate long-term.
In many cases you can proceed to installation, but production readiness typically requires acceptance testing, baseline configuration, monitoring setup, and verification of update procedures. A controlled validation step is strongly recommended to reduce rollout risk.
Even if you plan a quick rollout, the minimum readiness package should include: confirmation that the shipped firmware/software matches the baseline; verification that network and protocol configurations match the environment; confirmation that diagnostics are visible to your monitoring systems; validation of a controlled update (or at least a dry-run procedure); and confirmation that your staff knows how to respond to the device’s health alerts.
Before finalizing a purchase for Kony DBX, confirm these conditions/requirements with the supplier and document them in your acceptance plan:
To operationalize these conditions, build an acceptance plan that includes both device acceptance and system acceptance. Device acceptance typically verifies the unit’s behavior in controlled conditions. System acceptance verifies the integrated behavior: how the device interacts with your network services, upstream/downstream systems, monitoring tooling, and update workflow.
Also consider a phased deployment strategy. If the device is new to your environment, you can reduce risk by deploying to a limited set of sites or a pilot environment first. During pilot, you validate: performance under your typical traffic patterns; error handling and recovery; operational visibility; and your ability to perform updates safely. If issues appear, you address them before scaling.
If your project uses facilities or partner networks in a localized service area—often described as nearby—the decision dynamics can differ from centralized procurement. For example, local teams may depend on faster RMA logistics, clearer installation handover documentation, and training materials that fit existing maintenance routines. In such cases, you should ask whether the supplier can support your local operational cadence with consistent spare availability, predictable service response, and localized documentation in the language your technicians use during commissioning.
Even without naming specific cities or countries, the core principle remains the same: evaluate Kony DBX not only as a product, but as a maintainable system component within your “nearby” operational ecosystem.
Localization can also affect practical integration details such as lead-time variability, shipping constraints for regulated equipment, local standards compliance, and availability of certified installation services. If you are deploying across multiple local teams, standardization becomes even more important: each team should follow the same installation checklist, configuration baseline, monitoring setup, and update process.
In localized contexts, it’s common that the “handover” documentation is the difference between smooth commissioning and repeated escalations. Therefore, ensure the supplier provides: concise installation steps, known pitfalls, wiring diagrams appropriate for your hardware version, and troubleshooting flowcharts. If the documentation is too technical but lacks operational guidance, local technicians may rely on ad-hoc support requests, which delays operations and increases cost.
Localization also impacts how quickly you can rotate spares. If a unit fails, your ability to source an equivalent replacement quickly reduces downtime. Ask about spare parts lead times, whether spares can be ordered separately, and whether the supplier can guarantee revision-level equivalence for spares (so you don’t receive a different baseline that complicates field replacement).
To make these mistakes more actionable, it helps to consider the hidden failure modes that often occur:
Choosing Kony DBX responsibly comes down to evidence and governance: match interfaces, confirm environmental readiness, verify security and update behavior, and lock part numbers and revisions through the procurement process. By using structured supplier due diligence, a test-driven integration approach, and a documented acceptance plan, you can transform what might look like a simple procurement item into a reliable, maintainable part of your good system architecture.
Ultimately, the “defensible path” is the one that you can explain to stakeholders: engineering can point to interface compatibility tests and diagnostics validation; operations can point to health monitoring readiness and maintenance workflows; security can point to update authentication and access control evidence; and procurement can point to revision lock, warranty terms, and lifecycle commitments.
If you build that chain of evidence before deployment, you reduce the chance of discovering critical gaps after installation. You also increase the chance that your integration can be repeated across additional sites, partners, or deployment waves—because the process becomes a repeatable asset rather than a one-off effort.
For objective background on risk management and cybersecurity guidance that often informs procurement requirements, consult NIST publications available at nist.gov and relevant ISO/IEC standards for quality and risk practices. These sources provide general frameworks; specific Kony DBX requirements should always be validated against the supplier’s official documentation for the exact revision you intend to deploy.
While general standards provide useful principles, device procurement requires detailed, device-specific evidence. Make sure any internal standards mapping exercise (e.g., mapping device features to a security framework) uses the supplier’s documented behavior and test evidence. If documentation is incomplete, treat it as a risk and address it through targeted tests or contractual requirements.
Create a controlled update plan: define maintenance windows, validate changes in a staging environment, back up current configurations/log baselines, and confirm rollback behavior if supported. Require release notes that describe impacts to interfaces, diagnostics, and behavior.
In addition to the basic process, mature organizations define what “success” looks like after an update. Success criteria typically include: device health indicators returning to normal state within an expected time window; no unexpected changes to protocol behavior; diagnostic log formats remaining parseable (or versioned); monitoring dashboards continuing to show accurate status; and network services behaving consistently. If you have strict uptime requirements, you might also define criteria for “safe partial degradation,” such as allowing updates only when certain dependencies are available or when critical services are not actively processing sensitive transactions.
Update governance also includes a security verification step. If updates are signed, you should validate that the device verifies signatures and rejects invalid images. If updates require keys or credentials, document the credential handling procedure and ensure you align with your internal secret management practices. Also define how you audit update actions: who approved, when it happened, which version was installed, and whether rollback occurred.
Finally, define a rollback procedure that is practical for field or operations teams. Rollback is only useful if it is safe and if you have the required materials (e.g., the older firmware image) and the operational steps are documented. If rollback is not supported, your plan should explicitly treat that as a risk and rely on staging validation and canary deployments to reduce exposure.
Your plan should include functional workflows, interface connectivity checks, fault injection scenarios (within safe boundaries), diagnostics verification, monitoring visibility confirmation, and verification of update/rollback procedures. Acceptance criteria should be measurable—e.g., expected log fields appear, error states trigger expected behavior, and health indicators reflect real device status.
To make the acceptance test plan more robust, include at least these categories of test cases:
Also ensure that your acceptance test plan includes objective pass/fail criteria and explicit evidence capture steps. Evidence capture often means: exporting log samples, recording diagnostic counters, capturing network traces when permitted, documenting firmware versions installed, and saving screenshots or reports for dashboards and alerts. Without evidence capture, disputes occur when acceptance fails, because teams cannot easily prove what happened.
Lastly, define how acceptance test failures are handled. Not all failures are equal; some may be configuration issues, others may be genuine device defects, and others may be integration gaps between multiple systems. Your acceptance plan should specify triage paths, including whether you can use workarounds temporarily, when you must treat an issue as a blocker, and what changes require re-testing.
This guide synthesizes what people commonly discuss in Justworks Reddit threads and turns it into practical, objective criteria for SMB decision-making. Background context is provided on what Justworks is, why HR/payroll conversations appear on Reddit, and how to evaluate providers without relying on hearsay or pricing rumors.
Kony DBX helps organizations plan, deploy, and optimize data handling for reliable application workflows. This guide explains what “Kony DBX” typically refers to in enterprise contexts, outlines selection and integration considerations, and offers practical steps and requirements. It also addresses governance, performance, and operational risks in an objective way, including an expert Q&A section for decision-makers.
This guide explains Kony Dbx in practical terms—how it fits into modern product workflows, what to evaluate when sourcing, and which conditions typically matter before purchase. Objectively, “DBX” concepts often relate to signal/processing or equipment configuration layers, while “Kony Dbx” is commonly used as a product/series name in procurement discussions.
Cash Management Services for Corporates help firms centralize liquidity, streamline payments, and improve visibility across banking relationships. This guide provides objective background on cash management, key service capabilities, and typical procurement considerations, focusing on corporate treasury needs such as payment controls, forecasting support, and operational governance.
Payment Processing Solutions are integral to modern commerce, facilitating seamless transactions between buyers and sellers. Deploying efficient systems allows businesses to handle payments securely and quickly across various platforms, providing a crucial backbone for ecommerce and traditional retail settings. This article delves into the nuances of payment processing, offering a thorough understanding for businesses looking to enhance their transaction capabilities.
Payment processing solutions are essential systems enabling businesses to handle transactions electronically, facilitating seamless financial activity. With the growing shift towards online and contactless payments, understanding these solutions is vital for businesses to stay competitive and ensure customer satisfaction. This guide explores the intricacies of payment processing, dissecting its components and how businesses can leverage these systems to enhance efficiency and security.
This guide delves into the realm of Payment Processing Solutions, essential for businesses enduring the challenges of efficiently handling financial transactions. These solutions integrate secure, fast, and customer-friendly payment technologies that are crucial for modern commerce, whether in-store or online. By implementing tailored strategies, businesses can optimize operations, reduce costs, and enhance customer satisfaction through seamless payment experiences.
Payment processing solutions are integral to modern commerce, facilitating secure and efficient transactions for businesses worldwide. These systems handle the authorization, transaction, and fund transfer processes, ensuring a seamless experience for both merchants and consumers. From credit cards to digital wallets, they are the backbone of financial transactions, evolving rapidly with technology advances.