Kony Dbx can be a decisive choice when you need dependable system integration and maintainable operational workflows. This guide explains what “Kony Dbx” typically refers to in technical purchasing contexts, how buyers evaluate suppliers, and which requirements matter for installation readiness. It also outlines a comparison framework, sourcing steps, and conditions to help you assess fit objectively.
When people search for Kony Dbx, they are usually trying to solve a practical problem: selecting and integrating a system component or platform element that must work reliably in their existing environment. The very important early step is not price—it’s fit. Before you compare any price information or supplier offers, confirm compatibility with your infrastructure, your operational constraints, and your internal support model. If those fundamentals are missed, later “fixes” often cost more than the initial procurement.
Because your request includes supplier details and location-specific content placeholders, this guide focuses on objective evaluation criteria that remain valid regardless of where you source. If you later provide a specific city/country or vendor name, you can map these criteria directly to that context.
In many procurement situations, “paying twice” happens in three common ways: (1) you pay for a component that turns out to be mismatched to your environment, (2) you pay for integration twice because initial implementation lacked clarity, or (3) you pay for support and rework because operational handover was incomplete. The goal of this article is to help you prevent all three patterns by ensuring you verify what truly matters before you commit.
To make this practical, treat Kony Dbx like a contractually defined deliverable rather than a vague technical concept. Your early verification should therefore include the exact scope, the exact interfaces, and the exact ownership boundaries. This approach keeps procurement from becoming a “trust me” exercise and makes deployment outcomes easier to verify through acceptance criteria.
Finally, remember that “fit” is not just technical fit. It also includes organizational fit: whether your team can operate and maintain the system, whether your governance model can approve changes safely, and whether your business processes align with the operational realities of the new component. A perfectly compatible component can still create hidden operational costs if it lands in a team without the tools, training, or escalation channels needed for long-term success.
Kony Dbx is commonly referenced as a named item in sourcing workflows—often tied to a specific model family, configuration, or integration deliverable rather than a generic commodity. In procurement and technical deployment, such naming typically points to one or more of the following:
To avoid confusion, buyers should treat Kony Dbx as a reference term requiring confirmation of the exact scope: version/configuration, interface requirements, licensing boundaries, and acceptance criteria.
Because named technical items can be ambiguous across suppliers, your job is to convert the term into a precise procurement description. The easiest way to do this is to require suppliers to answer questions like: Which version is included? Are there optional modules included by default? What interfaces are enabled? What are the documented prerequisites? What exclusions are assumed?
Also consider that “Kony Dbx” could represent different levels of completeness depending on how the supplier packages it. Some suppliers may quote the component only; others may bundle installation, integration, configuration, and even partial application development. When you compare offers without normalizing scope, you accidentally compare different projects rather than different prices.
From a buyer’s standpoint, the most important background concept is that procurement needs verifiable scope. Verifiable scope means you can point to documented artifacts (release notes, interface specifications, configuration guides, installation guides, runbooks, and test scripts) and verify that the deliverables include those artifacts. Without this, “Kony Dbx” might be a placeholder name that hides missing items.
In addition, you should be aware that named components often come with licensing rules. Even if license terms are not the headline cost, they can affect the long-term total cost. For example, some configurations might require additional licenses for higher environments (staging vs production), additional user seats, or additional features that are not obvious from a simple unit price.
“Price information” without scope is an incomplete comparison. Industry practice favors evaluating the total cost of ownership (TCO) for at least the first deployment cycle, because integration and onboarding effort frequently dominate early costs.
From an industry-expert perspective, the very defensible evaluation approach includes three layers:
If you are comparing multiple suppliers, ensure that every quotation defines the same deliverables. Otherwise, you might think you are comparing price, when you are actually comparing different projects.
To expand that idea into a repeatable method, use a structured normalization process:
Risk evaluation should be explicit and documented. For example, if one supplier assumes your team will prepare an environment and another supplier assumes they will, you should treat that difference as a material scope gap. If you only compare “total price,” you might accept the cheaper supplier’s assumption—and then you pay the integration gap later as internal labor or additional vendor work.
Another critical dimension is change risk. Some systems require ongoing configuration tuning during early go-live. If a supplier’s contract does not clearly cover modifications, re-testing, and re-validation during stabilization, you may end up paying additional fees repeatedly. Therefore, evaluate not only whether the system “works initially,” but also how the supplier handles adjustments and stability improvements during early operations.
Lastly, consider that the cheapest quote can hide long-term costs such as limited support hours, slow escalation, or lack of proactive maintenance. These costs often show up as operational downtime, emergency patching, or delayed fixes. Good evaluation accounts for those outcomes upfront by checking warranty and support terms, incident response expectations, and patch cadence.
Supplier evaluation should be evidence-based. Use documented proof rather than marketing claims. Here are the practical checks that typically matter very when sourcing something like Kony Dbx for integration:
These elements help you judge whether a supplier can support Kony Dbx long enough to meet operational outcomes—not just to “ship” the initial component.
To make the checklist more actionable, consider requiring evidence in the form of deliverable samples. For instance:
Also consider verifying the supplier’s internal capability to maintain quality. Ask who the named technical owners are for architecture, deployment, and support. Ask whether their delivery team uses version control for configuration artifacts. Ask how they manage repeatability: are there scripts, templates, and standardized deployment steps to reduce “hero work” and manual errors?
For change management, you want more than a generic statement like “we support upgrades.” You want detail such as:
For support structure, ensure clarity between incident response and change requests. Incident response handles “something is broken now.” Change requests handle “we want new capability or a planned modification.” If the contract blurs the lines, your team may struggle to route issues correctly and may incur extra costs for handling routine changes.
Security posture should include more than patching. You should ask about access controls for vendor support activities, audit logging practices, and how credentials are handled. If vendor engineers need elevated access during deployment or troubleshooting, define how that access is granted, time-limited, and revoked. Also check whether they follow secure handling for configuration and secrets (e.g., using vaults rather than storing credentials in plain text).
Finally, check whether the supplier can communicate clearly. Integration projects often fail in the “requirements clarity” stage because documentation or communication is incomplete. A supplier who has a mature documentation practice and an explicit acceptance framework is more likely to deliver predictable outcomes.
Your instructions include a localization rule: when a keyword includes {city} or {country}, replace it with “nearby.” In this version, no explicit city/country was provided, so the guide is written to be applicable for procurement and deployment in any region “nearby” your organization—meaning you should still consider logistics, delivery lead times, service coverage, and language requirements based on your local context.
In many regions, buyers also face operational nuances such as procurement lead times through local distributors, differences in standard documentation language, or on-site scheduling norms. If you later specify a location, you can refine the acceptance checklist and supplier selection accordingly.
Even when you do not specify a location, you should still evaluate location-related factors as a general category. These factors influence schedule, cost, and risk:
One subtle but important point is how local procurement processes interact with technical deployment. For example, some organizations require internal security reviews or vendor onboarding steps before any deployment work begins. If the contract timeline does not include those steps, suppliers might count on access to your environment before you are ready. This mismatch causes schedule slip that can look like “technical problems” even when the root cause is procurement process timing.
Therefore, treat location as part of an end-to-end plan, not as a logistics footnote. You want the supplier’s timeline to explicitly accommodate your internal procurement steps and your local operational calendar. If the supplier cannot flex around local blackout periods, release windows, or maintenance schedules, you should clarify expectations early.
Lastly, consider travel and remote collaboration realities. If your local team requires on-site training but the supplier’s nearest technical team is far away, you might receive a quote that assumes remote training only. If you later discover the training was not adequate, the “fix” becomes costly. So ensure your training deliverables match the operational reality of your region and your team’s working constraints.
Even when the Kony Dbx item itself is correct, failures often occur because teams did not prepare the environment and governance around it. Treat the following as conditions/requirements to confirm before procurement finalization:
Confirming these in writing reduces integration friction and supports smoother go-live.
To expand on each condition:
Interface clarity should include not only “what endpoints exist,” but also how the system behaves under stress. For example, you want to know:
If the supplier cannot provide clear interface behavior, you should treat it as a deployment risk. Integration projects often require joint testing sessions once the systems encounter real data patterns. Clear error-handling behavior reduces time spent “guessing” during those sessions.
Environment compatibility requires attention to details like patch levels and dependency versions. Even “minor” version mismatches can produce confusing failures. Make compatibility requirements explicit by requesting a compatibility matrix. If you are running virtualization or containerized infrastructure, include those layers as part of compatibility evaluation as well.
Operational ownership includes two layers: operational monitoring ownership and configuration/change ownership. Monitoring ownership means who sees alerts, who investigates, and who declares incidents. Configuration/change ownership means who can modify settings, how approvals are obtained, and how changes are tested before deployment to production.
Acceptance tests should be measurable and testable by both parties. A good acceptance test plan includes:
Documentation and training need to be role-based. A developer who installs is not the same as an operations engineer who monitors. Training and documentation should therefore match who will use the materials. For example, operations training should focus on dashboards, alert interpretation, troubleshooting flows, and escalation. Developer training (if applicable) should focus on integration code behaviors, configuration parameters, and environment differences.
In addition, the best suppliers provide “knowledge transfer artifacts.” These include architecture diagrams, configuration parameter lists, and troubleshooting decision trees. If those artifacts are missing, knowledge transfer becomes a series of conversations rather than a stable foundation for operations. Over time, this causes operational dependence on the supplier’s personnel—exactly the opposite of what you want.
This section translates the evaluation approach into a usable workflow. It is intentionally practical and avoids assumptions about your vendor or region.
Ask suppliers to specify the exact configuration and what is included. Your goal is to convert “Kony Dbx” into a precise procurement description: version/config, interfaces, included components, excluded components, and documentation package.
To define scope properly, you should not stop at product naming. Instead, require suppliers to provide a scope breakdown that includes:
Additionally, scope should include exclusions. Exclusions prevent misunderstandings. Examples of common exclusions include: “We do not provide network configuration changes,” “We do not provide data mapping,” “We do not modify your existing authentication system.” If exclusions are not stated, you may discover them later when you request a modification.
Finally, define the “acceptance environment.” If the component will be installed in a staging environment, confirm what “staging” means in your context. If it will be installed directly in production, you must treat risk differently and tighten acceptance and rollout control measures.
Request quotations that separate:
This allows you to compare apples to apples rather than relying on a single total number.
To strengthen the procurement process further, ask suppliers to include:
Many cost surprises happen when an initial quote assumes the buyer will perform tasks that the buyer did not realize were excluded. A clear separation of work types prevents this. If you want to avoid paying twice, insist that supplier quotes explicitly state what you are paying for and what you are responsible for yourself.
Also consider that pricing may differ due to delivery model. A supplier might quote a low cost but require your team to provide significant engineering time or internal resources. Another supplier might quote higher cost but include more labor, tools, or testing. Both can be valid, but your evaluation should capture the total effort involved.
From a procurement governance standpoint, line-item pricing helps you negotiate: you can compare support terms, training deliverables, and acceptance test coverage separately. This reduces the risk of locking into a contract structure that you later find difficult to adjust.
Run an environment fit check. Require documentation for supported platforms, compatibility constraints, and prerequisites. If any requirement is unclear, treat it as a procurement risk until clarified.
A practical approach is to create a technical requirements checklist and use it in supplier Q&A. Include items like:
Then compare supplier claims against your actual environment. If you discover mismatches—like your runtime version is one step behind the supported list—make that a formal risk. You can resolve it through environment upgrades, alternative configuration, or a different supplier offering. But the key is to resolve before signing.
It can also help to run a small proof of concept (PoC) if the scale is manageable. A PoC does not need to be a full production deployment; it needs to validate compatibility and integration behavior. If a PoC reveals fundamental problems, you save time and avoid expensive rework.
However, even PoCs should have acceptance criteria. If you simply test “it starts,” you may miss runtime integration failure modes. Ensure PoC includes real interface tests, basic error handling, and monitoring verification. That reduces the chance that the PoC looks successful but production fails.
Agree on test plans. For example: what system behaviors constitute success, who executes tests, how defects are classified, and timelines for remediation.
This step is often where procurement meets engineering reality. To make acceptance criteria robust, avoid vague phrases like “installed and configured” unless they are tied to measurable outcomes.
Good acceptance criteria are commonly structured into:
Also define test ownership. Usually, the supplier runs certain tests, while your team runs others—especially tests tied to your production-like data flows. Joint testing helps but requires coordination. Define:
Test ownership clarity prevents “blame loops.” Without clarity, each party may argue the other should test first, and the project loses time. Clear rules reduce schedule drift and keep acceptance measurable.
Ensure knowledge transfer includes configuration runbooks, monitoring guidance, and escalation procedures. A strong supplier provides materials that your team can use without “tribal knowledge.”
Operational handover should be treated as a deliverable with measurable outputs. Consider requiring:
Knowledge transfer is not only about a training session. It’s also about ensuring your team has the operational artifacts needed to maintain the system independently. If your team cannot run basic troubleshooting without vendor involvement, that is a sign of insufficient handover.
Also ensure the supplier communicates how they will handle security updates and planned changes. If updates require your team to schedule downtime or to apply patches in a specific order, those dependencies must be documented. Otherwise, you can end up with “surprise” maintenance windows that conflict with business priorities.
Finally, validate that documentation is current and matches the actual deployed configuration. If the documentation is generic or outdated, it will mislead your team. Request evidence that the documentation reflects the release deployed in your environment.
If your context allows, use a phased deployment and observe operational stability before full-scale adoption. Keep a rollback plan and change calendar to prevent unsynchronized modifications during early production use.
A controlled rollout is a risk-management practice. Even if you have good acceptance criteria, real operational conditions often expose issues: unusual data patterns, network latency, integration edge cases, or unanticipated user behaviors.
Use rollout phases such as:
Define what conditions trigger a pause or rollback. Rollback criteria might include repeated critical errors, failure to meet performance thresholds, inability to process critical business transactions, or security-related anomalies.
Also coordinate change calendars. If multiple teams are deploying related components at the same time, you risk creating a system where you cannot isolate which change caused an issue. A controlled rollout benefits from change window discipline. If your organization cannot enforce strict change windows, require at least a short period where only the Kony Dbx changes are active and other changes are frozen.
For rollback, confirm whether rollback is a vendor-supported operation and what data impact it can have. Some systems can roll back binaries but leave configuration in an altered state. You want clarity on whether rollback restores a previous configuration snapshot and how data integrity is preserved.
After go-live, compare actual outcomes to the acceptance criteria and the baseline assumptions. Document issues and improvements to support future upgrades or expansions.
Post-deployment review should not be an afterthought. It is a disciplined loop for learning and improving. You can structure the review around:
Then feed the findings into a continuous improvement plan. If there are gaps, prioritize fixes. Some fixes might be quick configuration adjustments; others might require code changes, documentation updates, or process adjustments.
Finally, ensure that your future upgrade planning uses the learnings. If your integration behavior depends on specific configurations, document them. If certain monitoring gaps were discovered after go-live, update the runbooks and dashboards accordingly. This reduces repeat “integration pain” in future lifecycle phases.
The table below is designed to help you compare suppliers and delivery models objectively. It intentionally avoids external links and focuses on procurement-relevant dimensions. Replace the bracketed fields with the details you receive in quotations.
| Evaluation Category | Supplier Option A (Fill In) | Supplier Option B (Fill In) | What Good Looks Like |
|---|---|---|---|
| Defined Scope of Kony Dbx | [e.g., version/config, included components] | […] | Explicit version/config; clear inclusions/exclusions; complete documentation pack |
| Price Information Structure | [base + integration + support breakdown] | […] | Line-item quotation enabling like-for-like comparison |
| Warranty and Support Terms | [duration, response commitments] | […] | Defined SLAs; realistic escalation steps; documented responsibilities |
| Integration Approach | [on-site/off-site, timeline, deliverables] | […] | Written plan with milestones and acceptance gates |
| Acceptance Testing Ownership | [who tests, defect handling rules] | […] | Measurable criteria; shared test plan; remediation timeline |
| Security and Access Controls | [patch approach, access model] | […] | Patch/vulnerability handling process; least-privilege access model |
| Training and Handover | [sessions, materials, runbooks] | […] | Role-based training; actionable runbooks; transfer of ownership artifacts |
| Logistics “nearby” Considerations | [lead time; on-site coverage] | […] | Clear delivery timeline and support coverage for your region |
To use the table effectively, do not treat it as a static artifact. Turn it into a decision tool:
When a supplier provides incomplete answers in one column, that often signals a hidden gap elsewhere. For example, vague acceptance criteria might mean you will not get measurable deliverables. Vague support terms might mean escalations are unclear. Use the comparison table to surface those gaps early.
Also, ensure you verify that both suppliers plan their delivery using comparable milestones. If Supplier A plans a milestone named “Integration complete” but includes only configuration while Supplier B includes interface testing and performance validation, those milestones are not equivalent. Your comparison should reflect real deliverables, not just shared milestone names.
When experts evaluate systems in a category associated with Kony Dbx, they typically focus on the “hidden work” that buyers underestimate:
In practical terms, a slightly higher upfront cost can be cheaper if it reduces integration cycles, rework, and downtime during early adoption.
To elaborate on these specialist concerns:
Interface edge cases matter because real systems do not behave like test scripts. You need to know how the integration component handles unusual conditions. Specialists often test scenarios such as:
If the supplier cannot provide guidance for these cases, you should plan for additional joint testing sessions after initial integration. Those sessions have cost and schedule impact. So evaluate whether the supplier’s acceptance plan includes validation for edge cases or whether it only covers “happy path” flows.
Operational observability is frequently underestimated. Specialists want to see that monitoring is actionable. Logging that is too verbose can drown your team in noise, while logging that is too sparse makes troubleshooting impossible. Good observability practices include:
Upgrade path is not only a vendor lifecycle question; it is a governance and operational continuity question. Specialists ask: If we upgrade later, will our configuration be migrated safely? Will we need downtime? Will our monitoring and runbooks remain accurate? Are there breaking changes in interfaces that we must adjust?
To evaluate upgrade path readiness, require supplier documentation on:
Governance determines whether operational changes stay controlled and documented. Specialists look for how your organization will handle version control, approval workflows, and documentation updates. If governance is weak, even a good deployment can become fragile over time due to uncontrolled configuration changes.
Therefore, define governance expectations early. Decide who approves changes, what documentation must be updated after changes, and what the standard operating procedure looks like. This ensures Kony Dbx remains maintainable long after go-live.
In summary, specialists look for maturity across technical behavior, operational readiness, lifecycle planning, and governance. These are the factors that separate stable deployments from recurring rework.
These errors are frequent in procurement and are especially costly when the supplier’s quoted scope is not aligned with the buyer’s expectations:
Adopting the step-by-step guide above is the very direct way to prevent these issues.
To make these mistakes easier to avoid, here are deeper explanations and practical countermeasures:
Mistake 1: Comparing total price only When buyers compare only total cost, they often ignore the structure of the quote. One supplier might include integration and testing in the price, while another might price those tasks separately. Or a supplier might include only the component but not the operational handover. The result is that “cheaper” can become more expensive after you pay for missing work.
Countermeasure: normalize quotations using a template and ensure each deliverable category is explicitly listed.
Mistake 2: Skipping environment validation Environment validation includes OS/runtime compatibility, network readiness, and dependency versions. Skipping it is risky because many failures emerge only when the component interacts with your specific environment. If issues appear late, you may need to change infrastructure or redo integration work.
Countermeasure: require a compatibility matrix and run a pre-deployment fit check. If needed, run a PoC with acceptance criteria.
Mistake 3: Accepting vague delivery statements Delivery statements like “installed and configured” are not enough. They don’t tell you whether interface behaviors are correct, whether logging and monitoring are in place, or whether acceptance testing passed under real conditions.
Countermeasure: insist on measurable acceptance criteria and define how evidence will be collected and reported.
Mistake 4: Underestimating training needs Training should match who will operate and maintain the system. If you only train a small group or train the wrong roles, you create operational bottlenecks. Over time, troubleshooting becomes dependent on the supplier’s expertise.
Countermeasure: require role-based training and deliver runbooks that support independent troubleshooting.
Another common mistake is not defining escalation paths and severity definitions clearly. When incidents happen, if severity levels are unclear, you can get slow response times or arguments about whether a situation counts as an incident. This becomes costly because downtime and customer impact accumulate while responsibility is debated.
Countermeasure: include an escalation matrix in the deliverables and align it with your internal incident management process.
Also consider the mistake of not aligning your internal change governance with the supplier’s delivery timeline. If your organization’s approvals take longer than the supplier expects, the supplier might proceed with assumptions that later prove wrong. Alternatively, if your team cannot freeze changes during rollout, you may not isolate the causes of issues during pilot phases.
Countermeasure: plan governance and change windows explicitly, and build them into milestone timelines.
Kony Dbx is typically used as a specific referenced item in technical sourcing. The precise meaning can vary by vendor and configuration, so you should request a clear scope definition: version/config, included components, interfaces, and documentation deliverables.
If you want to avoid ambiguity, ask suppliers to respond with a structured “scope confirmation” document. A scope confirmation document often lists included modules, excluded items, dependencies, and assumptions. This helps you ensure every offer is describing the same thing, even if the suppliers use different naming conventions.
Ask for line-item quotations that separate base cost, integration services, installation, training, and support terms. Compare like-for-like deliverables and confirm acceptance criteria in writing before committing.
Also ask for a summary of assumptions and a statement of what is included vs excluded. Then evaluate whether your internal resources will be required to cover any excluded tasks. Sometimes a cheaper vendor quote can require you to provide internal engineering time equivalent to what the more expensive vendor priced as part of integration services. Your decision should capture both monetary cost and internal effort.
Yes. Request evidence of relevant implementation experience, documentation maturity, support escalation structure, warranty/support coverage, and a written integration plan including acceptance testing responsibilities.
To strengthen this further, request sample deliverables. Sample runbooks, sample test plans, and sample configuration documentation help you judge whether the supplier can provide actionable operational artifacts—not just high-level documentation.
Confirm interface specifications, environment compatibility, operational ownership, measurable acceptance tests, and knowledge-transfer deliverables. If any condition is unclear, treat it as a procurement risk until resolved.
A useful practice is to maintain a “deployment readiness” log. When each condition is verified, mark it complete with evidence references (e.g., compatibility matrix, environment configuration screenshots, acceptance test scripts). This provides a traceable audit trail for decision-making.
Timelines vary based on environment complexity and scope definition quality. Use a written milestone plan and require suppliers to align estimates to specific deliverables and acceptance gates rather than relying on calendar-only promises.
Integration time depends heavily on the “unknowns” discovered during fit validation, data mapping readiness, and interface edge case testing. If your scope definition is incomplete, integration timelines become unpredictable. That’s why the evaluation and scope confirmation steps matter: they reduce the number of surprises that appear during integration.
Acceptance testing should define measurable outcomes: correct interface behavior, error handling, logging/monitoring requirements, and stability checks under representative workloads. Also agree on defect severity definitions and remediation timelines.
Additionally, acceptance testing should verify operational readiness. That includes verifying dashboards display correct information, alerts trigger appropriately, and runbooks contain troubleshooting steps that match real log outputs. If monitoring and runbooks are not tested, your acceptance might pass technically while operations later struggles.
Prioritize operational handover: runbooks, configuration guidance, upgrade/change procedures, and support responsibilities. Ensure the supplier documents how updates and patches are handled and what access your team will retain.
Maintainability also benefits from controlled change governance. Even with perfect documentation, if your organization applies configuration changes without review, you can create drift from the documented state. Therefore, define governance: version control for configuration artifacts, approval workflows, and periodic documentation verification.
For procurement and technical deployment practices, buyers often align with established frameworks and guidance from recognized bodies. While this article does not cite specific performance claims tied to Kony Dbx, the evaluation approach is consistent with widely used governance principles found in resources such as:
When you finalize supplier selection, request documentation that maps to your organization’s internal policies and relevant standards.
To make standards practical in procurement, consider asking suppliers to answer questions aligned with those frameworks. For example:
It’s also helpful to require a security review deliverable as part of the procurement lifecycle. Even a short security assessment can surface critical gaps like credential handling, insecure defaults, missing patch processes, or unclear access controls during support operations.
Responsible procurement also includes risk-based decision-making. If your environment is regulated or high-risk, apply more strict verification: evidence reviews, security questionnaires, and perhaps a security testing session. If your environment is less regulated, you can still apply baseline verification for access controls, logging, and vulnerability handling. The point is to treat security and risk as part of deliverables, not as a post-deployment afterthought.
Selecting Kony Dbx successfully is less about hunting a single number and more about confirming scope clarity, integration readiness, and supplier accountability. Use the comparison table to keep pricing discussions grounded in comparable deliverables, apply the step-by-step workflow to reduce deployment risk, and insist on measurable acceptance criteria. If you provide specific supplier names, exact configuration details, and any location-specific requirements, this guide can be adapted into a tighter procurement plan tailored to your scenario “nearby.”
When done well, procurement becomes a disciplined process that links commercial terms to technical outcomes. By verifying fit early, normalizing scope and price, and insisting on evidence-based acceptance, you prevent the most common failure modes: mismatched components, unclear responsibilities, incomplete handover, and hidden operational costs.
Ultimately, the best way to avoid paying twice is to make sure you understand what you are buying, what you are responsible for, what the supplier will deliver, and how you will verify success. If those elements are defined clearly—before purchase—you can make confident decisions and support stable deployment outcomes for the long term.
This guide explains what users discuss on Justworks Reddit, and how to interpret those experiences when evaluating a payroll and HR platform. Objectively, the conversation typically covers onboarding, pricing expectations, integrations, support quality, and real-world usability. It also highlights common pitfalls—like assuming Reddit feedback replaces formal vendor documentation or compliance guidance.
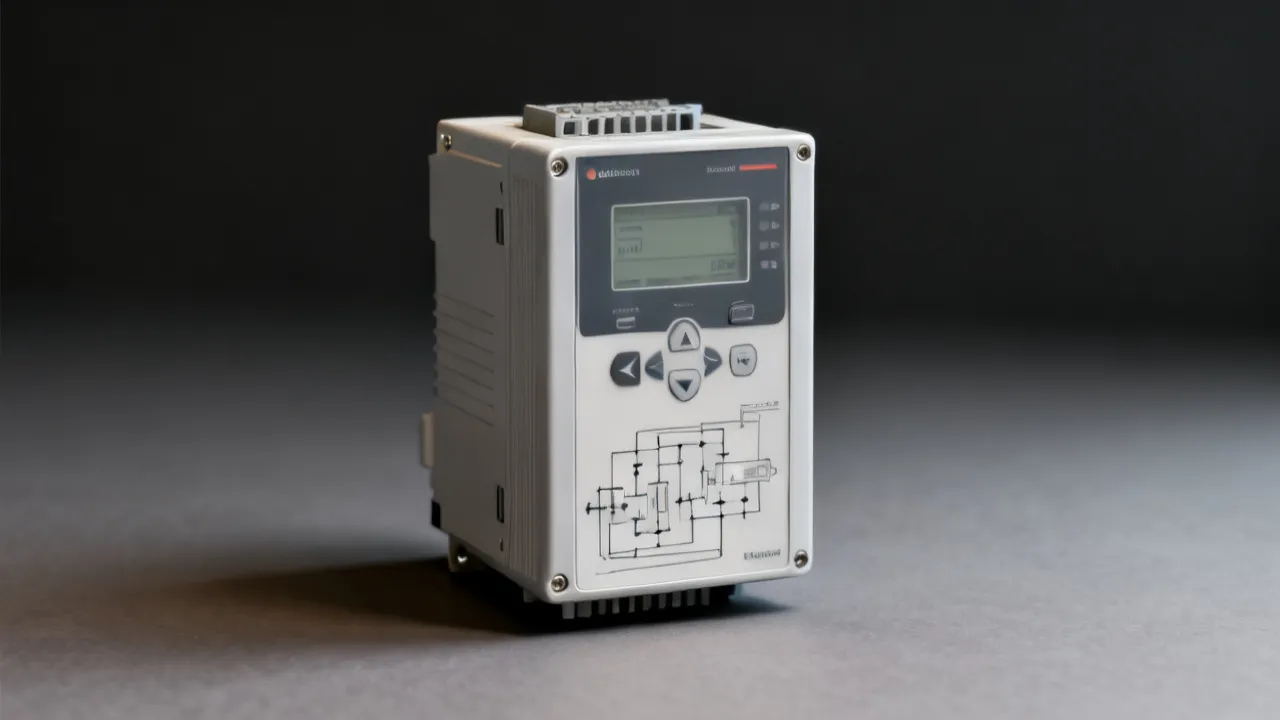
This guide explains how to evaluate Kony DBX for reliable performance, proper integration, and operational safety. It provides objective background on the “DBX” concept and the types of industrial systems that commonly use this naming style, then follows with expert selection criteria, sourcing considerations, and a conditions-focused setup checklist.